Services / AI governance and security
AI you can trust in production
Guardrails, evaluation and security controls that make AI safe, auditable and ready for real decisions.
Overview
Governance that lets AI move faster
AI changes the security picture. Prompts can be manipulated, models can leak data and agents can take actions nobody intended, while customers and regulators expect to know how AI decisions are made.
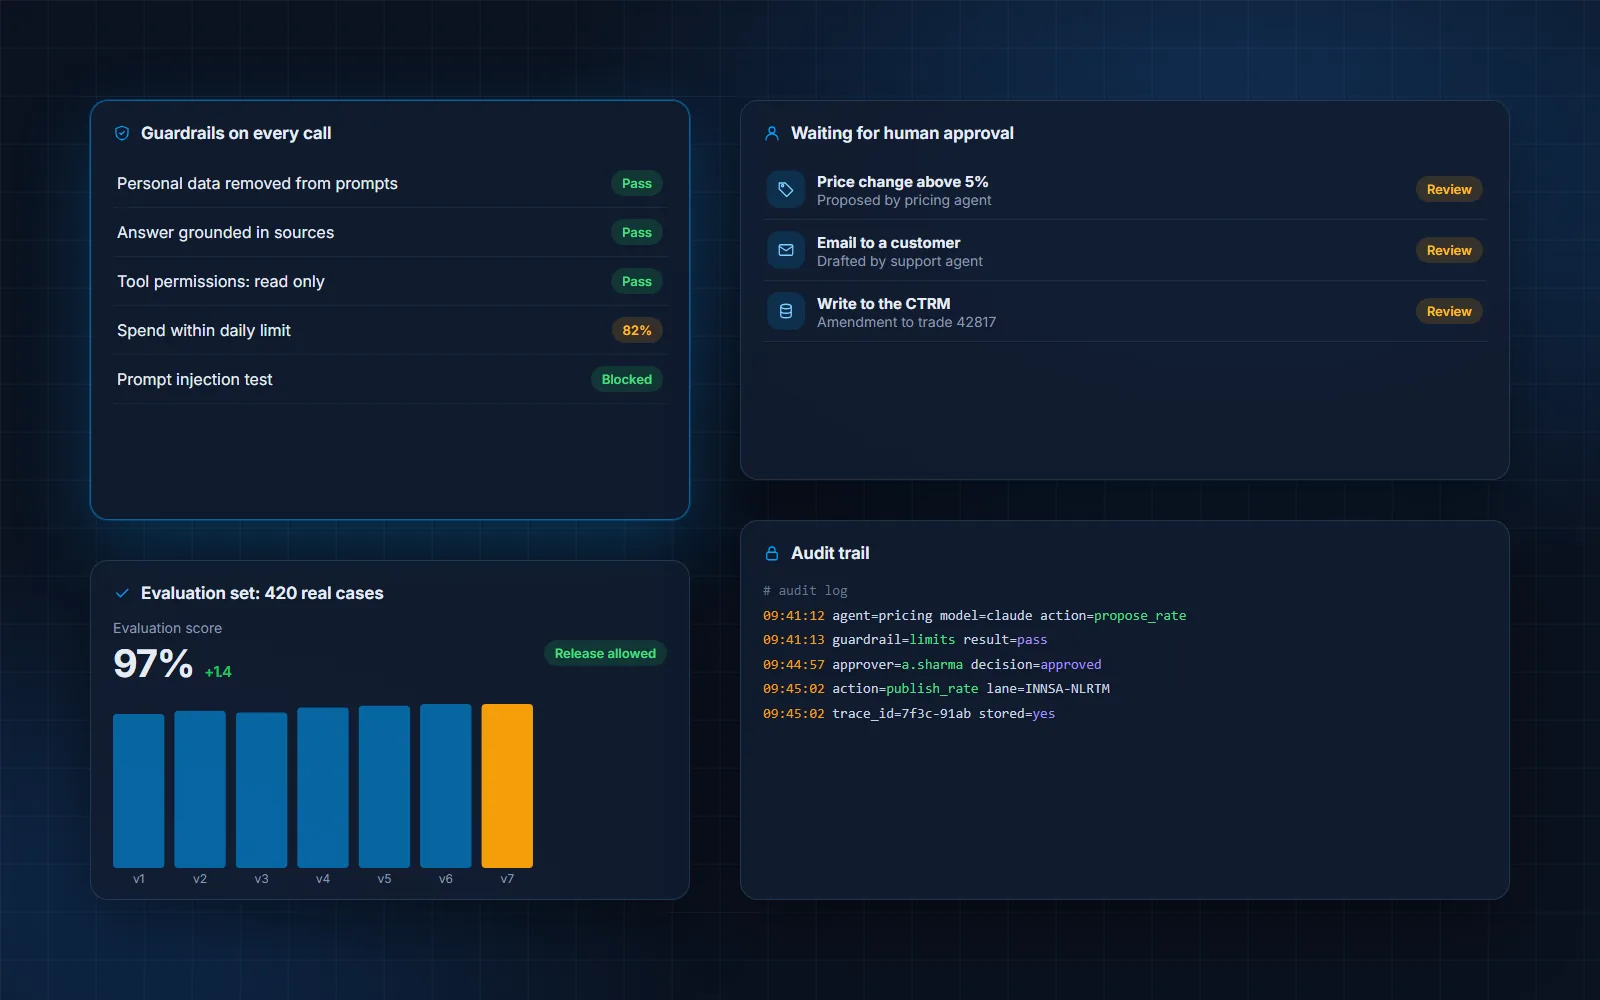
We put practical controls around AI systems: clear ownership, scoped permissions, input and output checks, evaluation before every release, and an audit trail showing which prompt, model and data produced each result. The aim is to let teams ship AI with confidence, not to slow them down.
The challenge
Where teams get stuck
- No audit trailWhen an AI result is questioned, nobody can show how it was produced.
- Prompt injection and leakageUntrusted text in emails, documents and web pages can steer a model if nothing stops it.
- Unclear accountabilityWhen AI acts, it is unclear who approved it and who owns the outcome.
Capabilities
What we deliver
AI risk assessment
Where AI is used, what it can touch and what could go wrong.
Guardrails and policy
Input and output checks, scoped permissions and approval steps.
Evaluation and red-teaming
Tests that catch regressions and unsafe behaviour before release.
Monitoring and audit
Every model call traceable: who, what, which prompt and at what cost.
Our approach
How we deliver it
01
Assess
Inventory AI use, data flows and permissions, and rank the risks.
02
Control
Guardrails, redaction, scoped permissions and approval for high-impact actions.
03
Test
Evaluation sets and red-team tests that run before every release.
04
Monitor
Logging, cost tracking and alerts so issues surface early.
Technology
What we build with
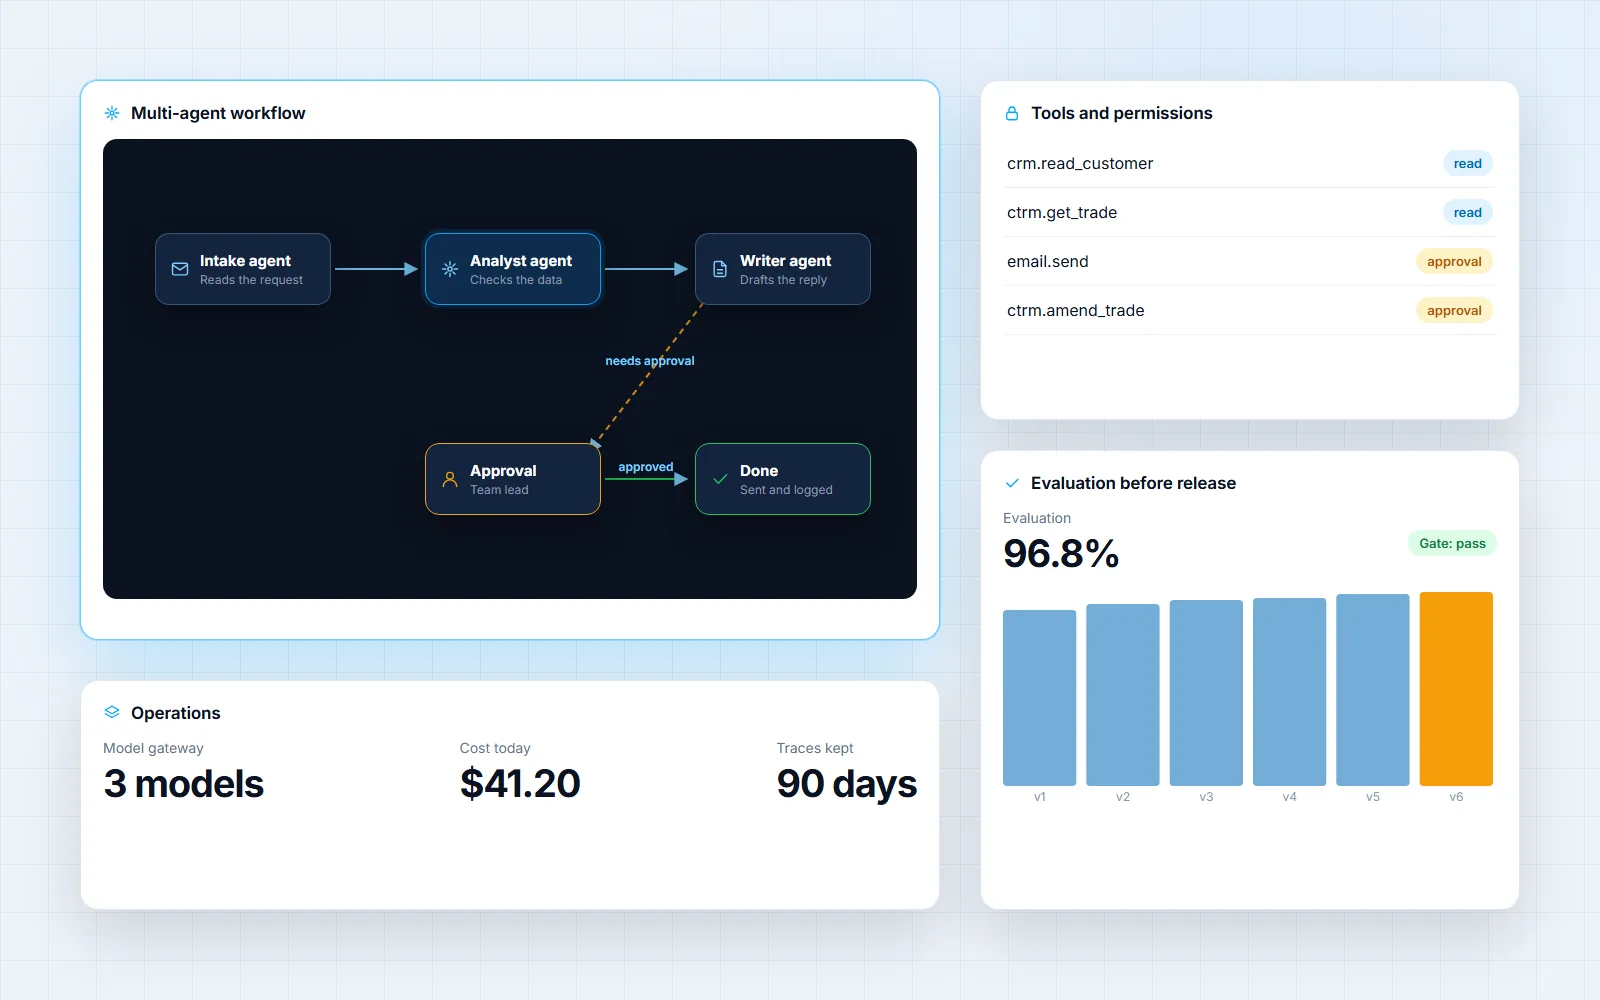
Human approval, evaluation sets and a full audit trail are built into our Agentic AI Accelerator. See how it works
Outcomes
What you get
Audit-ready AI
Every result traceable to its prompt, model and data.
Reduced risk
Known attack paths closed before anyone exploits them.
Faster approvals
Clear controls shorten security and compliance reviews.
Our accelerator
Agentic AI Accelerator
A ready-made foundation for AI agents that work inside your operations, with tool connections, human approval, evaluation and a full audit trail, adapted to your systems.
Questions we hear
Frequently asked questions
Can you review an AI system we already run?
Yes. We start with an assessment of models, data flows and permissions, then prioritise fixes by risk.
Do you cover wider cybersecurity?
Yes: secure architecture, identity and access control, and cloud security reviews alongside AI-specific controls.
Does governance slow delivery down?
Done well it speeds it up: clear guardrails let teams ship AI with confidence instead of debating every release.
Do you support regulated industries?
Yes. Controls are designed to produce the evidence auditors and regulators ask for.
Let’s talk
Have a project in mind?
Tell us what you are trying to achieve. The first conversation is free, you will leave it with practical next steps, and we reply to every enquiry within 4 hours.